On 17 November, CERT.LV urged organisations to check and update Citrix NetScaler ADC and NetScaler Gateway promptly. The two critical vulnerabilities are CVE-2026-107412 (CVSS 9.5) and CVE-2026-120868 (CVSS 9.3). The latter also affects the default configuration. Possible effects include instability or service outages.
What are the first fixed builds?
CERT.LV lists 14.1-73.57 for the standard 14.1 branch and 13.1-64.39 for the standard 13.1 branch. The thresholds are 14.1-73.58 FIPS for 14.1 FIPS and 13.1-37.293 for 13.1 FIPS and NDcPP. Upgrade to a vendor-recommended fixed build for your branch. If your version is unsupported, agree a migration to a supported release with your provider.
How should you organise the upgrade?
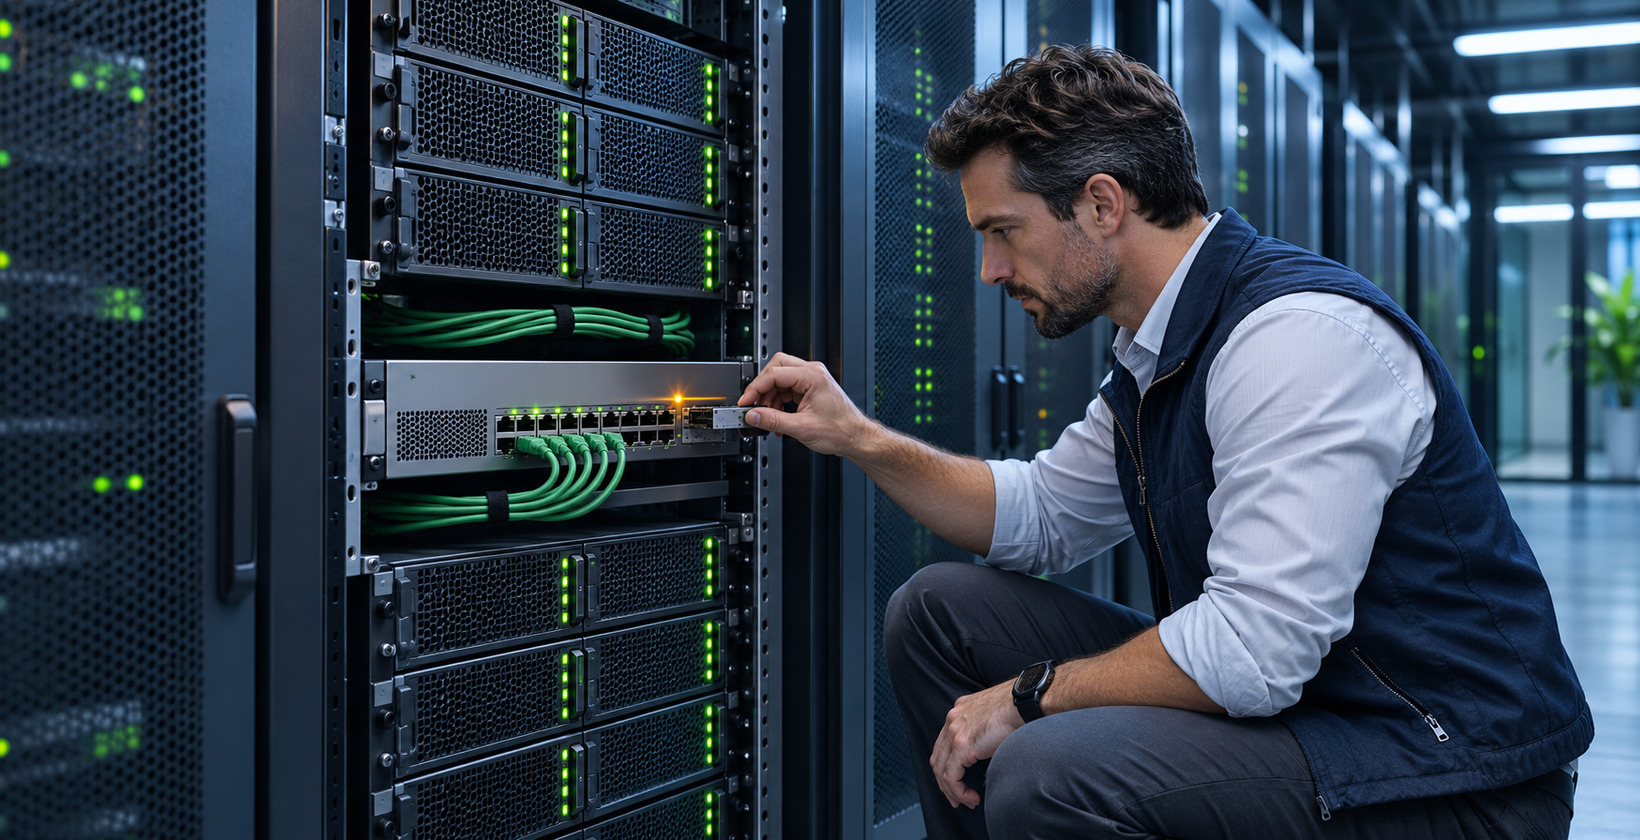
Inventory all appliances and their exact builds, including standby nodes. CERT-EU recommends prioritising internet-facing Gateway and AAA appliances. Before the upgrade, back up the configuration and agree a recovery plan. Afterwards, verify the build on every node, check system health and confirm that users can reconnect remotely.
What if a third party manages the service?
Request written confirmation of the branch and build before and after the upgrade. If you observe unexplained outages or access anomalies, preserve logs and involve your incident response team. Finding a vulnerable build alone cannot establish whether an incident occurred.
If you need outside help with IT operations, see business listings and services for businesses.
Comments
No comments yet. Yours could be the first!
Add a comment