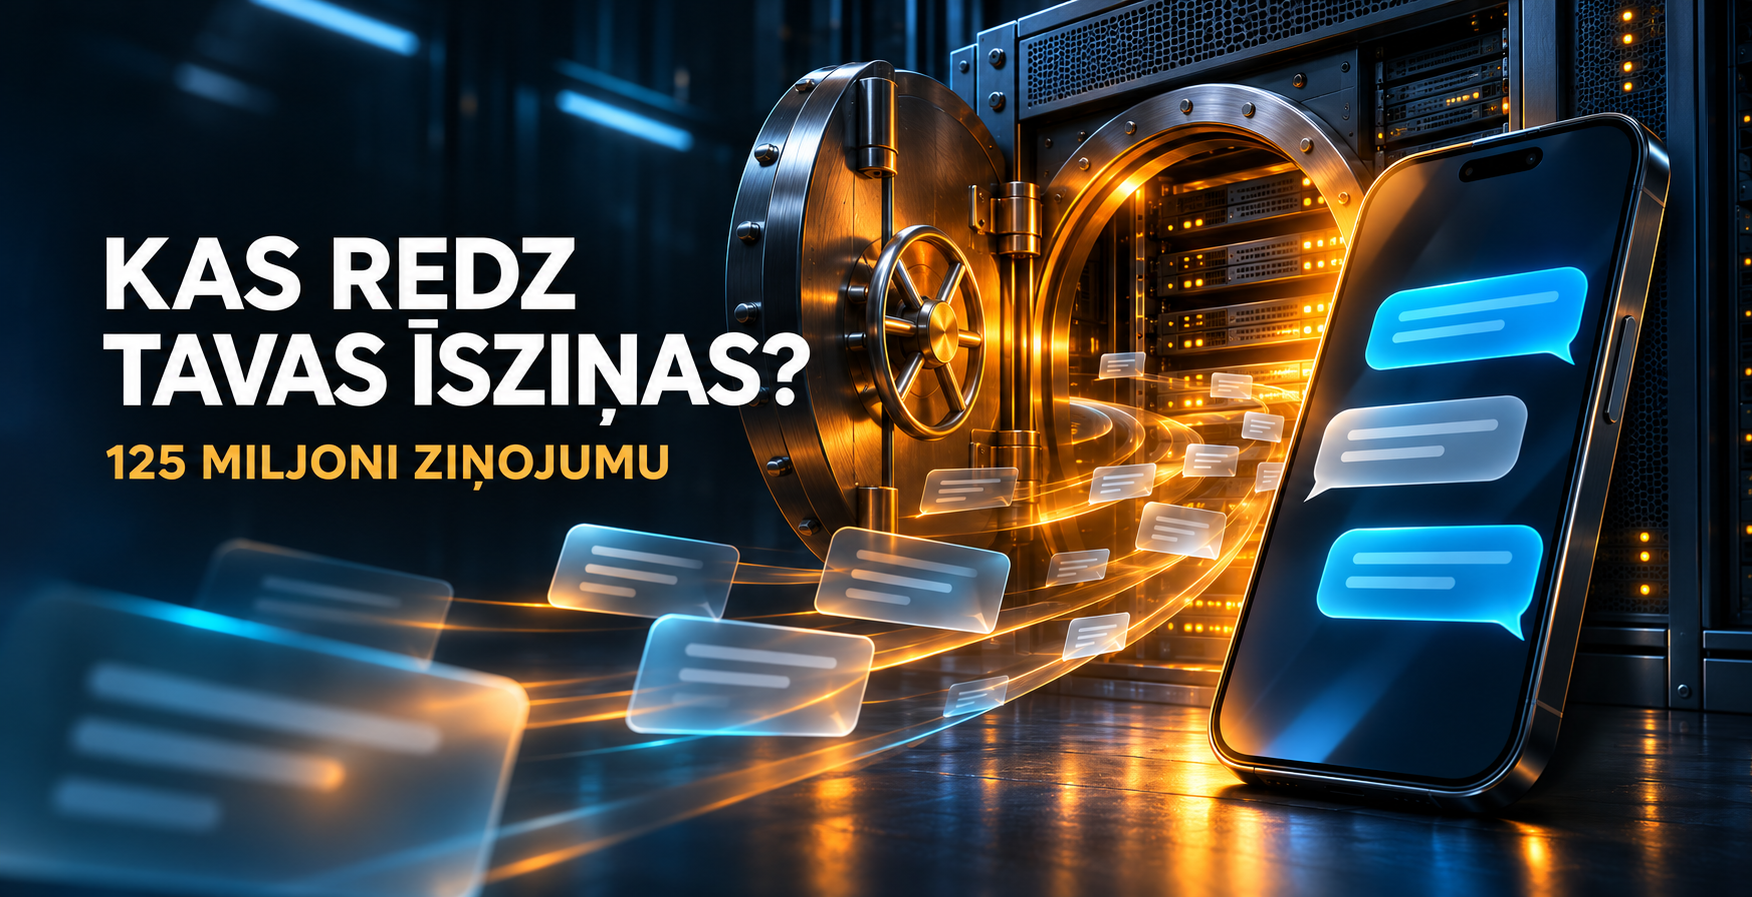
Cybernews researchers report more than 125 million texts in a publicly accessible CSC Telecom database, including telephone numbers, message contents and authentication codes. The researchers have no evidence of malicious access. Claiming that all these messages were stolen would therefore be unfounded.
What do the banks and CERT.LV say?
In its 11 November statement, SEB explains that it used the provider for general pension-fund messages, supplying telephone numbers and message text. Internet-banking codes and payment data were not sent through this channel. The bank says its systems’ security and customers’ funds are unaffected.
According to LSM, Swedbank has suspended use of the service, while CERT.LV has requested a detailed investigation. The scope of the incident is therefore still being established; one bank’s explanation cannot automatically be applied to another company’s customers.
What belongs in the outsourcing review?
EDPB guidance covers contractual requirements for security, sub-processors, incident assistance, and deleting or returning data when services end.
- Which providers actually receive customer data?
- What data do we share, how long is it retained, and how is deletion demonstrated?
- Who will notify us of an incident, and how can we check their explanation?
Our editorial recommendation: assign a responsible person and maintain a review sheet for each significant provider. Record the question, response, supporting document and next review date. A general promise of security is less useful than a specific, verifiable answer.
When should notification be assessed?
Latvia’s Data State Inspectorate explains that controllers must report a personal data breach without undue delay, where feasible within 72 hours of becoming aware of it. The exception is when risk to individuals’ rights and freedoms is unlikely. Missing information may be submitted in stages.
The practical conclusion: management should know not only whether messages arrive, but also what happens to the data afterwards. This review is useful even if the business does not use this particular provider.
When reviewing outsourced activities, explore services for businesses and business listings. Include data-processing terms alongside price when comparing proposals.
Official information sources
- SEB’s explanation
- EDPB: controller and processor responsibilities
- Data State Inspectorate: breach notification
Comments
No comments yet. Yours could be the first!
Add a comment